Extended Detection and Response (XDR)
Detect and respond, from inside the platform.
Cato XDR is the industry’s first SASE-based detection and response solution.
Today’s Challenges
Too many alerts, too little visibility.
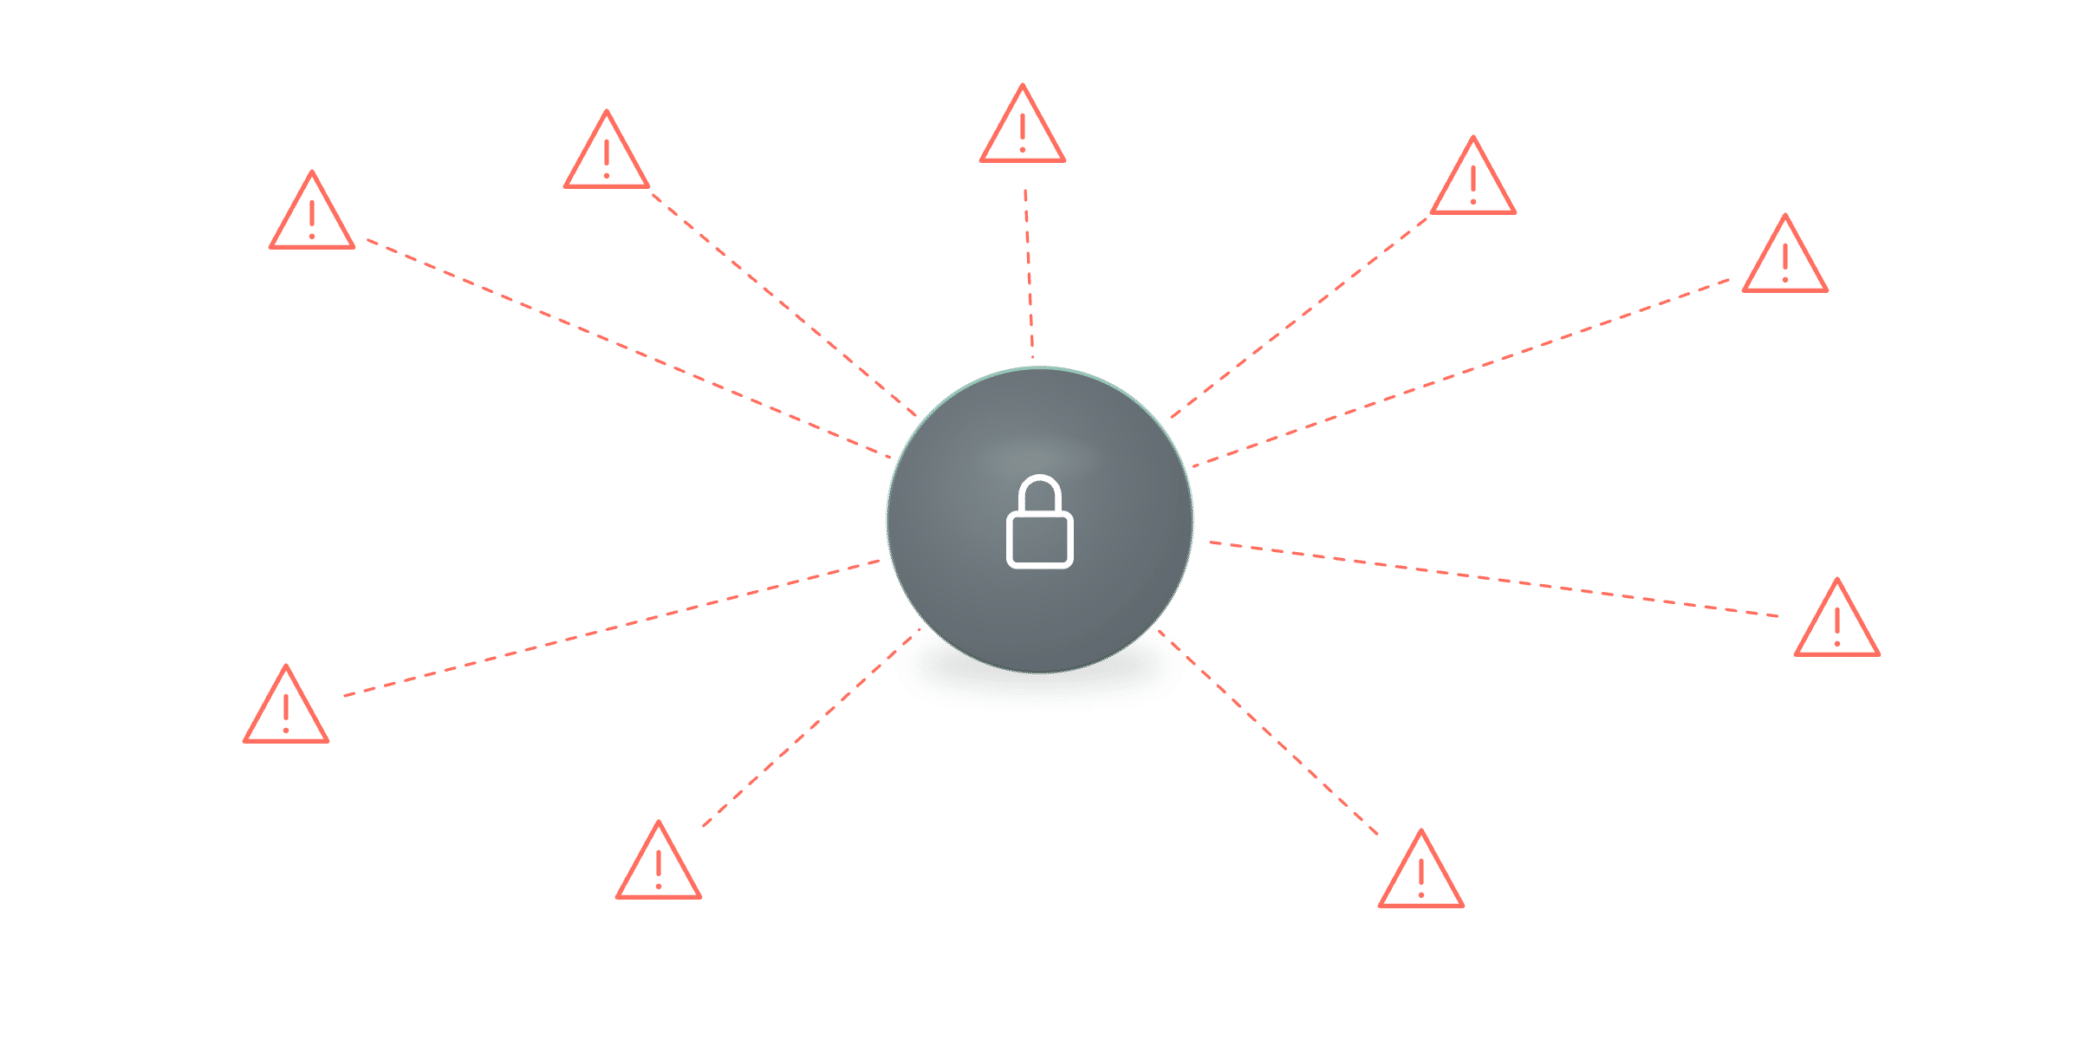

Alert overload
Security and operations sprawl across disconnected tools, making it hard to act quickly on threats, outages, and performance issues.
Alert overload
Lost context
Fragmented data
Our approach
Unified insights. Faster action.
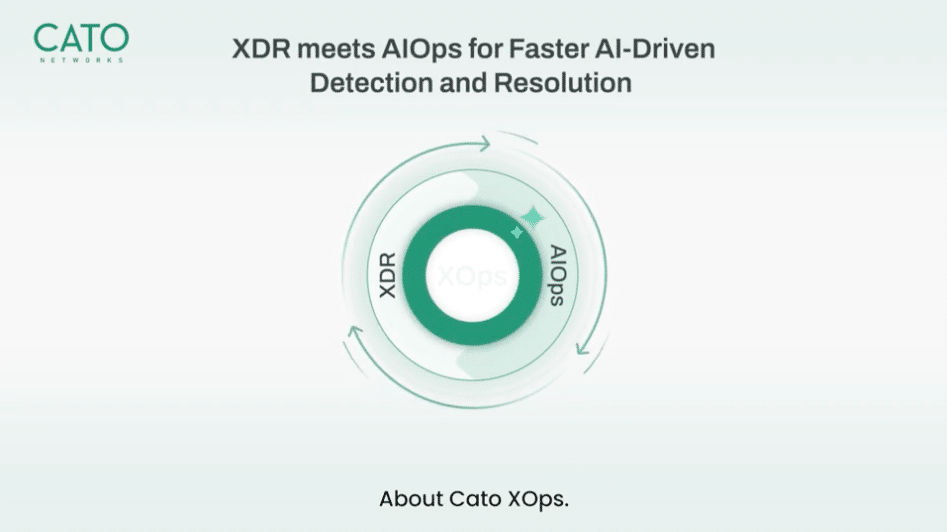
Modern IT teams face too many alerts and too little visibility across disconnected tools. Cato XOps converges XDR and AIOps into one unified insights layer, turning fragmented telemetry into prioritized stories that give teams shared context, faster investigations, and quicker resolution.


Operational Clarity
Turn fragmented alerts into clear, prioritized stories teams can act on faster.

Shared Context
Give security and operations teams one view across users, devices, apps, and infrastructure.

Faster Resolution
Speed investigation and remediation with correlated context, guided actions, and AI-driven insights.
White paper
The Industry’s First SASE-Based XDR Has Arrived
How it works
Extended Detection and Response (XDR) Capabilities
AI-powered threat stories
Turn alert overload into action
Cato XDR rolls raw security events into prioritized Threat Prevention incident ‘stories’, connecting the signals so teams act on what matters most.
Roll many block events into one incident
Promptly detect a compromised device
Take appropriate containment and remediation
AI/ML threat hunting
Smarter detection from native sensors
The threat-hunting engine continuously scans the data lake for anomalous indicators of resident threats the prevention layers didn’t block.
Continuously scan for resident, unblocked threats
Group signals into a single incident
ML risk-scores each incident to prioritize
UEBA
Investigate suspicious user activity
Cato XDR integrates User and Entity Behavior Analytics to identify unusual behavior that may indicate malicious intent.
Compare activity against a precalculated baseline
Alert on suspicious deviations as incidents
Detailed insights to judge malicious vs. benign
See it in action
Watch how Cato does it

Part of the XOps AI layer that boosts efficiency, speed and collaboration
Customer Stories
Customers love Cato
“
The XDR cards let us see all the data relating to an incident in one place, which is valuable. Seeing the flow of the attack through the network–the source of the attack, the actions taken, the timeframe, and more–on one page saves a lot of time. If a user has a network issue, I do not have to jump to various point product portals to determine where the application is being blocked.
Nick Hidalgo
VP, Information Technology, Redner’s Markets

Michael Wokusch
Senior IT Product Manager, TAG Heuer Porsche Formula E Team

Security Leader
Global Construction Company
Security Operations Leader
Global Data Services Company
Get a live demo
Secure every interaction across the enterprise, cloud, and AI with the only purpose-built SASE platform.
What to expect

15–30 minute session with a SASE product expert

Discuss your use cases and how we can help

Live product demonstration where applicable
Get Started
See Cato in Action
What’s new
Latest resources and insights
Solution Brief

White Paper
FAQS
Answers to common questions
How does Cato XDR use platform-native and external telemetry?3 questions
What is Cato XDR?
Cato XDR is Cato’s SASE-based extended detection and response capability. It uses telemetry from the Cato SASE Platform to detect suspicious activity, group related signals into prioritized incident stories, and help teams investigate and respond from the Cato Management Application.
How is Cato XDR different from traditional XDR tools?
Traditional XDR tools typically collect and correlate data from multiple products, often requiring separate sensors and integrations. Cato XDR is built into the Cato SASE Platform, giving it native visibility across networking, security, users, devices, and applications from a shared data lake. This enables richer context, AI-powered incident stories, and faster investigation without the complexity of integrating multiple point solutions. Cato XDR also works alongside existing SIEM and ITSM platforms, enriching your current SOC rather than replacing it.
Does Cato XDR work only with native Cato sensors?
No. Cato XDR is built on native Cato telemetry, giving it rich context across networking, security, users, and applications. At the same time, it can enrich its shared data lake with events from supported third-party sensors, including EDR solutions. This gives security teams a broader view of incidents while preserving the advantages of platform-native context.
How does Cato XDR support investigation and response?1 question
What does investigation and response look like in one console?
Cato XDR brings investigation and response together in a single workbench within the Cato Management Application. Security teams can investigate incidents, review risk scores, supporting evidence, and AI-generated recommendations from one console. From the same interface, they can take response actions such as updating security policies, blocking malicious traffic, or initiating supported remediation workflows without switching between multiple tools.
How does Cato XDR prioritize and explain threats?2 questions
How does Cato XDR reduce alert fatigue?
Cato XDR uses AI and ML to correlate related security events into prioritized, risk-scored incident stories. Instead of asking analysts to review every alert in isolation, the platform automatically connects related signals into a clearer incident story that explains what happened, why it matters, and where analysts should focus first. This helps security teams reduce alert fatigue and investigate incidents more efficiently.
How does Cato XDR use generative AI and MITRE ATT&CK?
Cato XDR uses generative AI to explain incidents in plain language and automatically maps them to the MITRE ATT&CK framework. Together, they help analysts quickly understand what happened, how the attacker operated, and what actions to take next, without manually stitching together data from multiple sources.
How does Cato XDR fit into XOps and get started?2 questions
What is the XOps AI layer, and how does it relate to XDR?
Cato XOps is the AI-powered insights layer of the Cato SASE Platform. It analyzes security and operational telemetry to deliver actionable insights for both SOC and NOC teams. Cato XDR is the security-focused capability within XOps, while AIOps focuses on operational visibility and troubleshooting. Together, they provide a unified view across users, devices, applications, and locations.
What does getting started with Cato XDR involve?
Getting started with Cato XDR is simple. It is built into the Cato SASE Platform, so there are no additional appliances, sensors, or infrastructure to deploy. Organizations can immediately benefit from native Cato telemetry while continuing to work with their existing SIEM and ITSM platforms.


